Neon sign reading 'Assessment Services' with a tagline above stating 'Evidence-first assessments. Defensible outcomes. Real impact.'

Securitique delivers rigorous, evidence-based assessments that produce defensible findings, accurate scores, and remediation roadmaps that drive real security improvement. We do not produce checkbox compliance reports. We do not produce checkbox compliance reports. We produce assessments that hold up to scrutiny.


Evidence - first assessments across four frameworks. Every engagement is governed by EFAS
A digital shield emblem with circuit patterns divided into blue and silver halves, surrounded by colorful circuit lines.
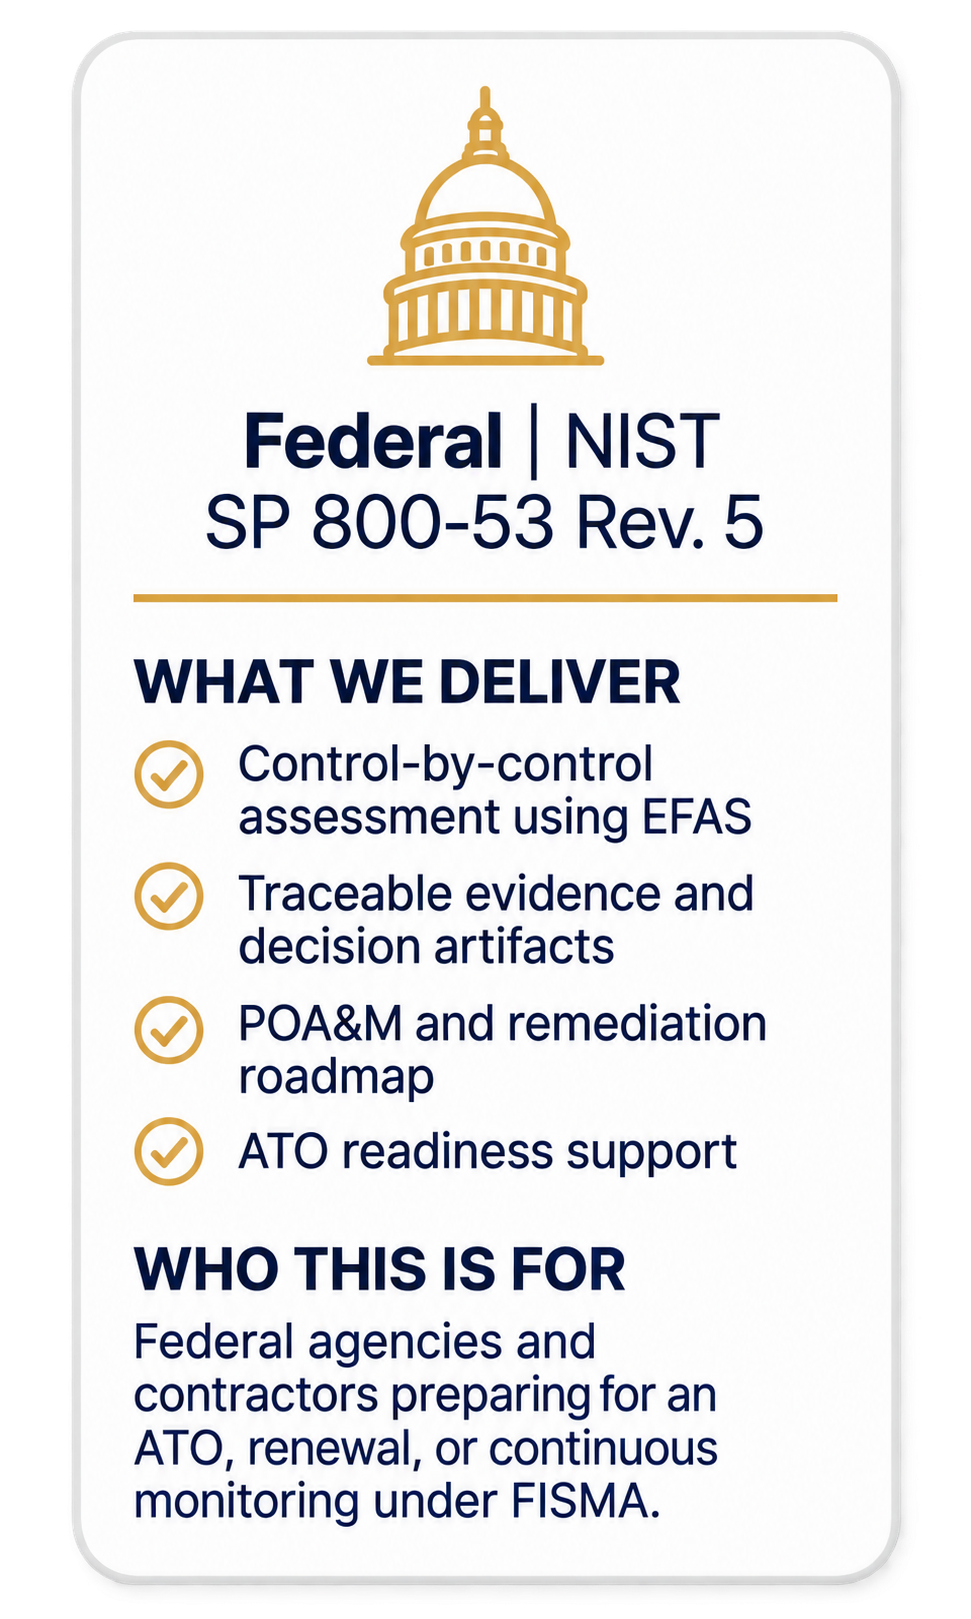
Info card from the U.S. federal government with a gold dome illustration at the top. It details deliverables for NIST SP 800-53 Revision 5, including control assessments, evidence traceability, POA&M and roadmap, and ATO support. It specifies the target audience as federal agencies and contractors preparing for ATO, renewal, or continuous monitoring under FISMA.
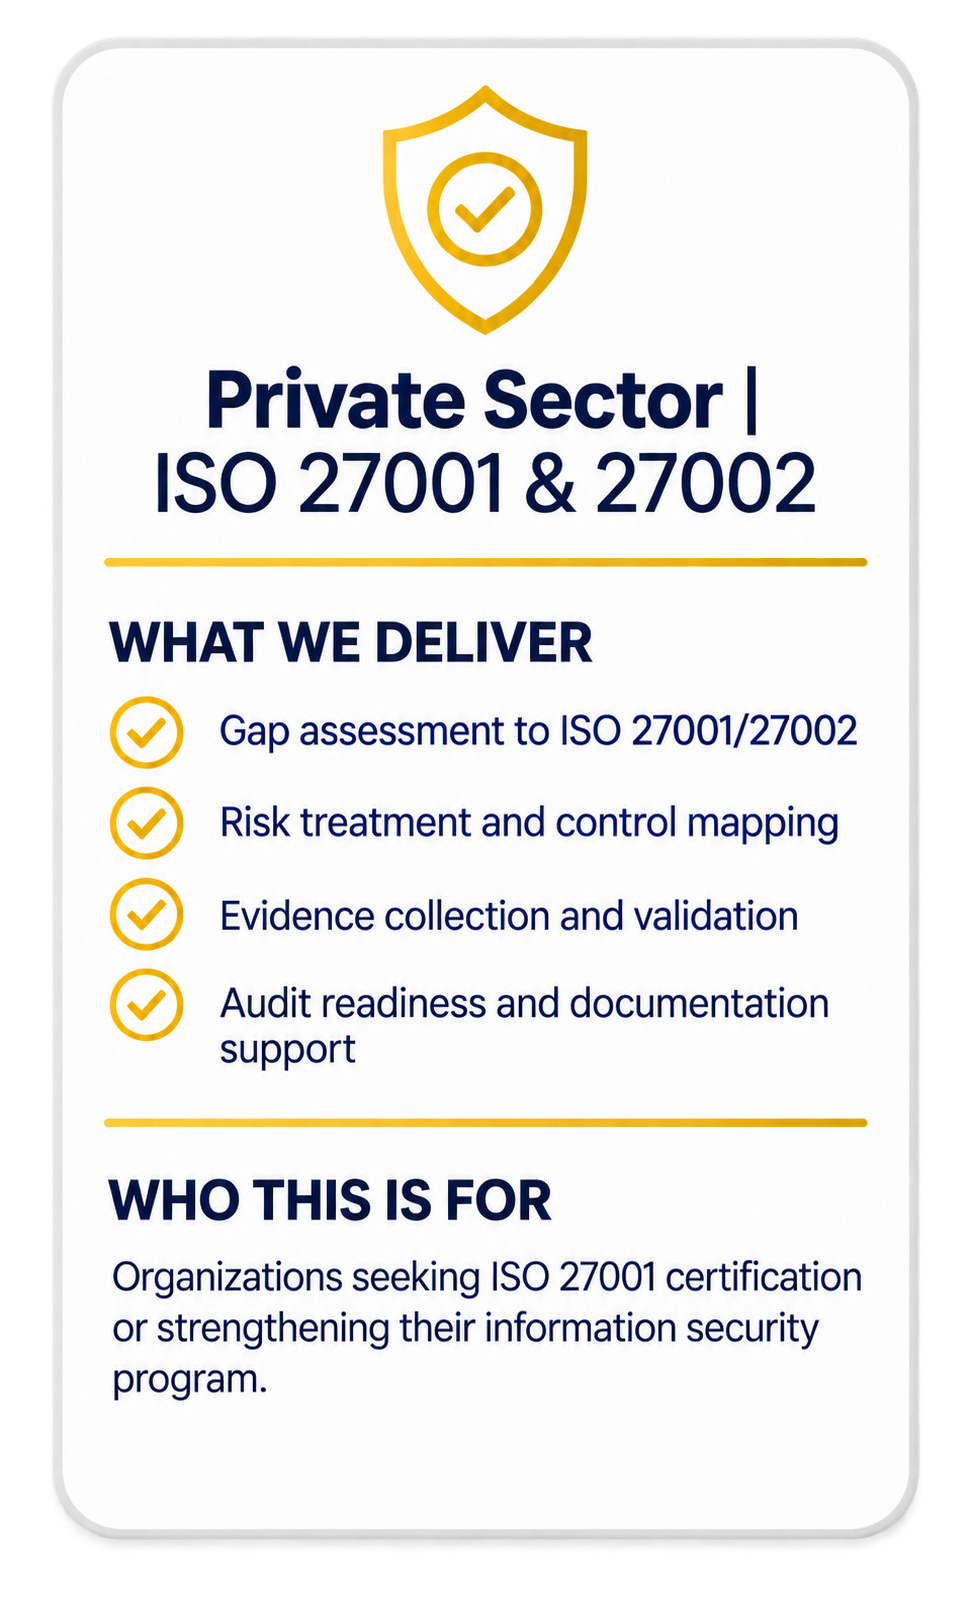
Sign promoting private sector ISO 27001 and 27002 compliance services with checkmarks and information on deliverables and target organizations.
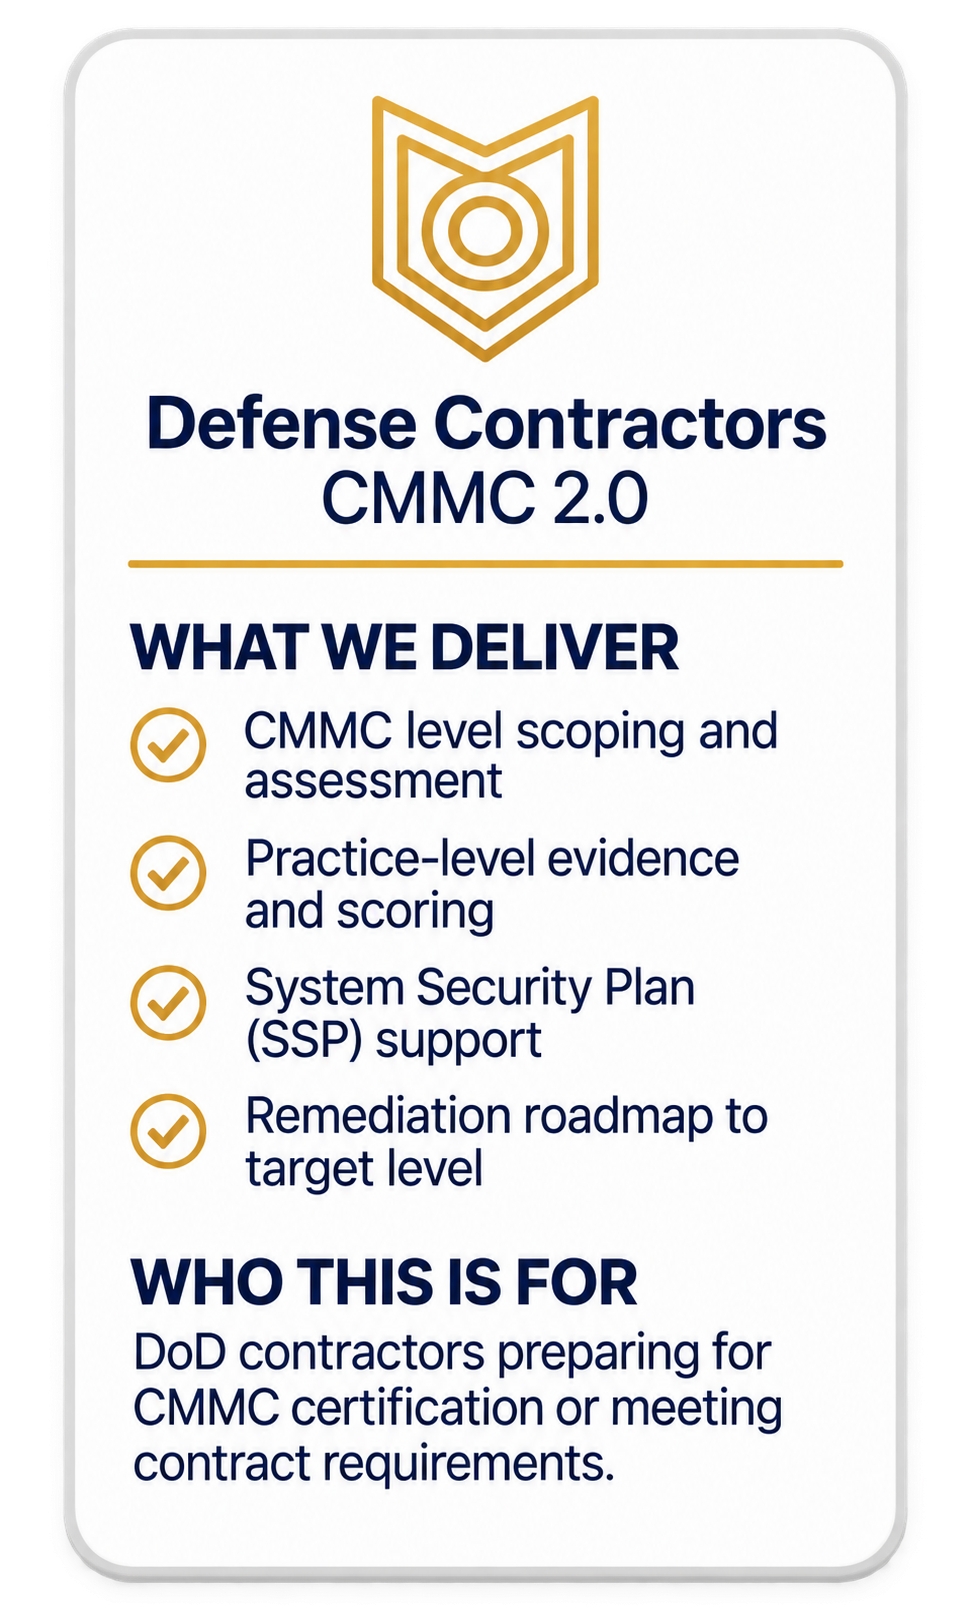
A vertical poster for Defense Contractors CMMC 2.0, detailing what they deliver and who it is for. The poster includes a logo at the top, followed by bold text stating 'What We Deliver'—listing CMMC level scoping and assessment, practice-level evidence and scoring, SSP support, and remediation roadmap. Below, it states 'Who This Is For', targeting DoD contractors preparing for CMMC certification or meeting contract requirements.
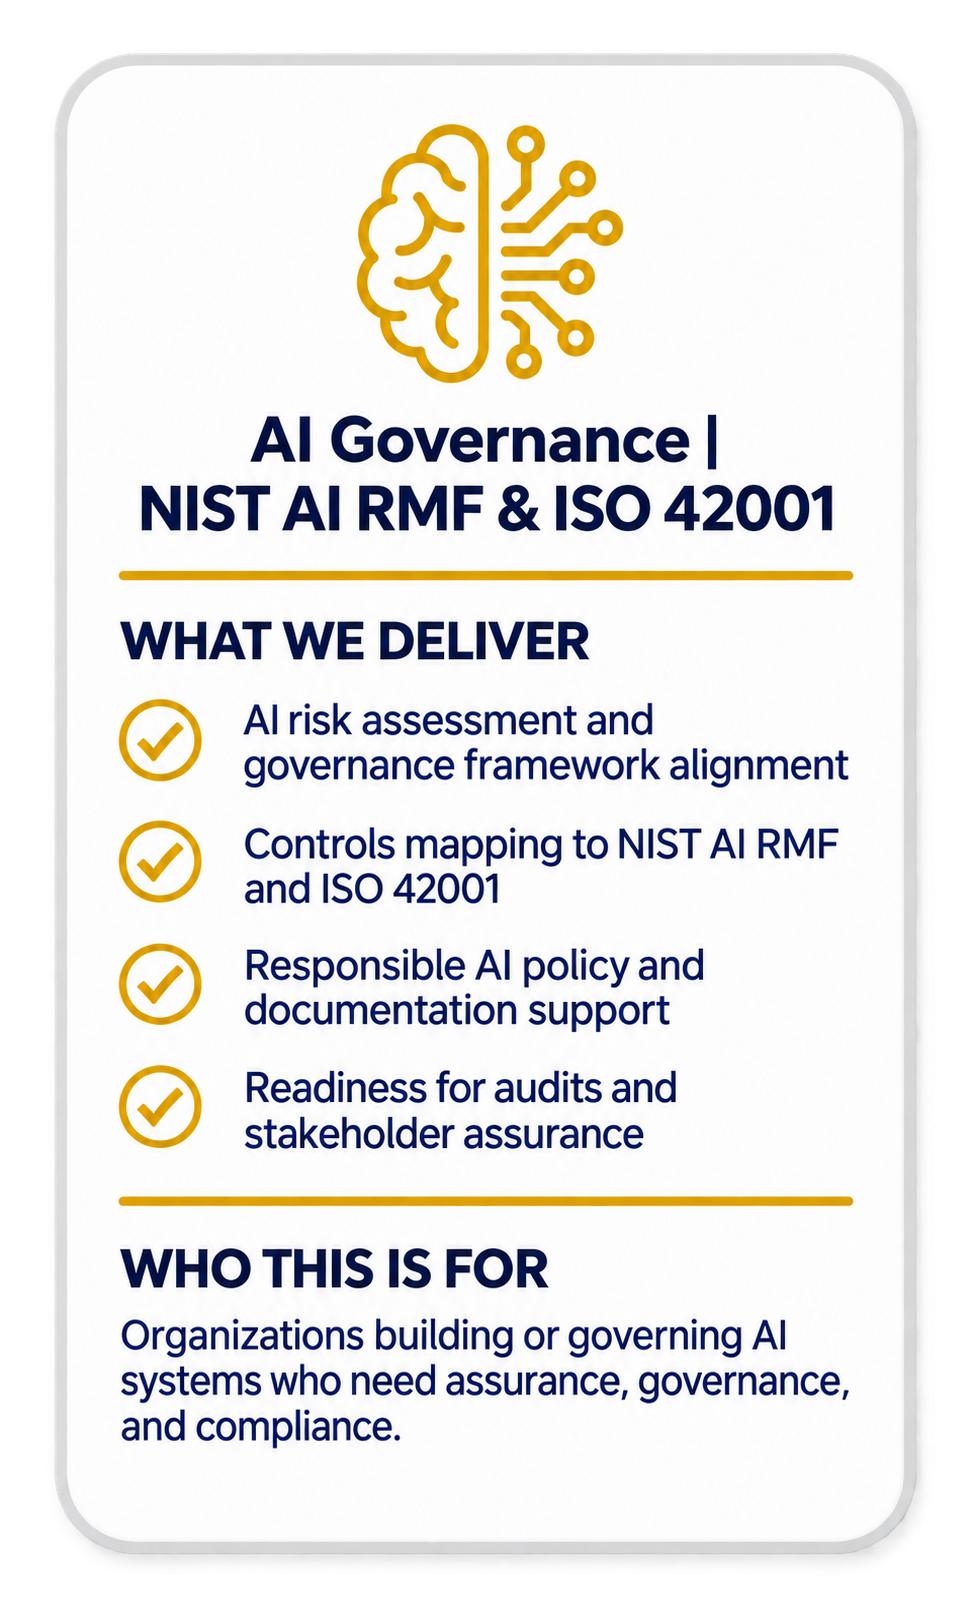
Information poster about AI Governance, listing deliverables such as AI risk assessment, controls mapping, responsible AI policy, and readiness for audits, targeted at organizations building or governing AI systems.

How Securitique Executes Within the Federal Risk Management Framework

Securitique assessments are designed to integrate directly into the NIST SP 800-37 Risk Management Framework lifecycle. Whether your organization is preparing for an initial ATO, renewing an existing authorization, or operating under continuous monitoring, Securitique's role is defined and deliberate.
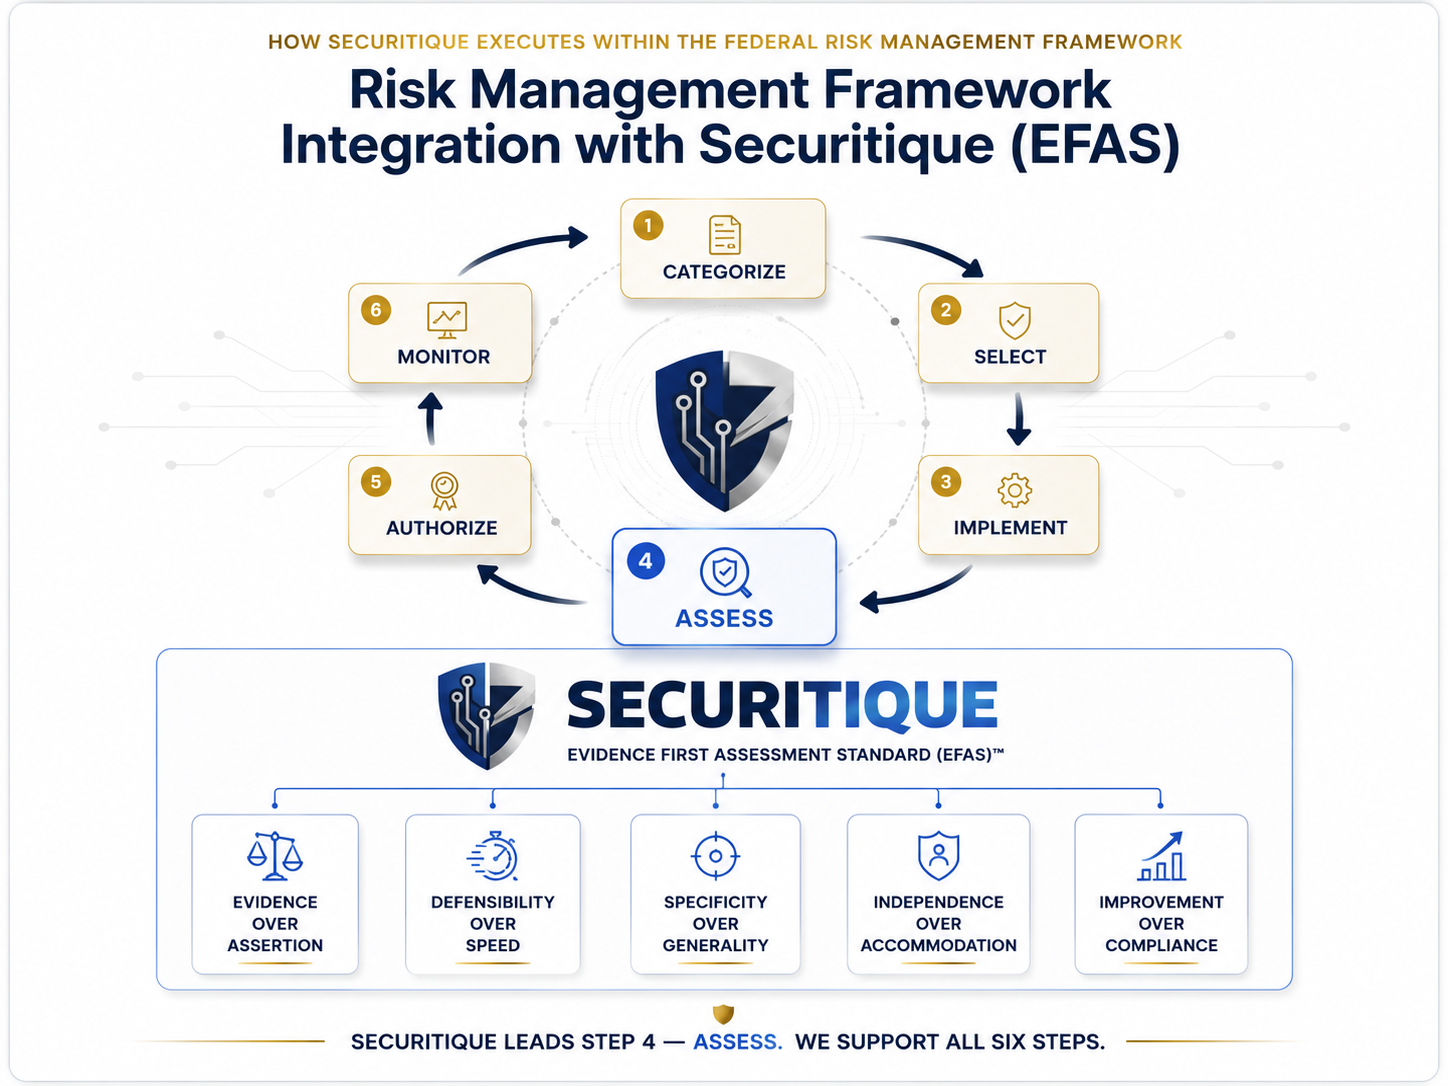
Diagram illustrating the process of Risk Management Framework integration with Securique (EFAS), including six steps: 1. Categorize, 2. Select, 3. Implement, 4. Assess, 5. Authorize, and 6. Monitor. The diagram emphasizes assessment as the fourth step and introduces the Securique evidence first assessment standards.

Request a Security Consultation

Complete the form to initiate a confidential discussion regarding your organization’s cybersecurity requirements.

Services

Filters

No results found

No results match your search. Try removing a few filters.